Framework coverage
Loaded, mapped, and hashed on ingest.
01
1,193 controls loaded
02
20 control families
The full NIST SP 800-53 Rev 5.1.1 catalog, mapped to the systems it applies to.
Access Control through Supply Chain Risk Management, every family covered.
03
4,376 assessment objectives
04
SHA-256 on every artifact
The SP 800-53A objectives that sit behind those controls, ready to be answered.
Every uploaded file is hashed on ingest, so evidence can be shown unchanged.
THE SIGNATURE EXPERIENCE
Your program is terrain, not a spreadsheet.

From control question to audit trail.
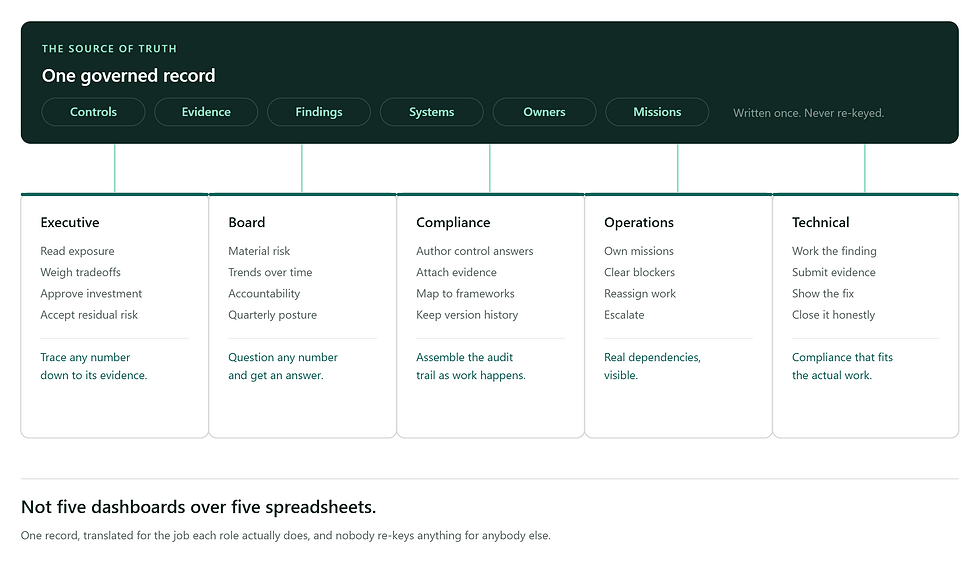
ATLAS walks your team through the control questions that actually apply, connects each answer to governed documents, correlates the supporting scan results, systems and owners, and keeps the version history intact — so when the assessor asks how you know, the answer is already assembled.
How it works
Four moves, one record.
01
Load the framework
02
Bring in what you already run
The control catalog and its assessment objectives arrive already structured and mapped to the systems they apply to.
Nessus, STIG, CKLB and XCCDF results land as findings against real systems, not as attachments in a folder.
03
Answer once, with the evidence attached
04
Export what the assessor reads
Each control question is answered against governed documents, and the answer keeps its evidence, its version history and its owner.
CKLB and POA&M come out in the formats your assessor already expects, each line traceable back to the record that produced it.
A claimed fix is not a validated fix.

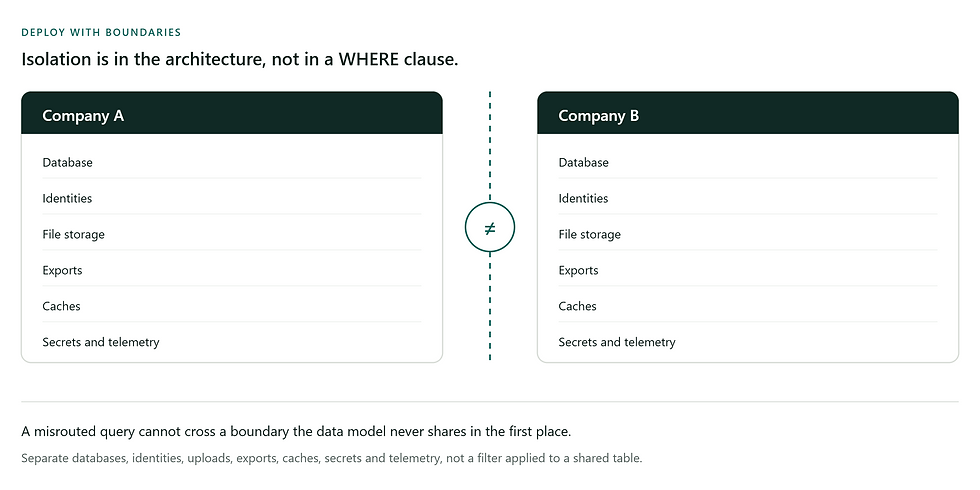
Each company is its own ATLAS. Separate databases, identities, uploads, exports, caches, secrets and telemetry — isolation as a boundary in the architecture, not a filter applied to a shared table.